'Plaintext' Exposed for 30 Seconds During Booting: Fatal Flaw in Aegis Ships and Stealth Fighter Cryptographic Equipment
A fatal flaw has been discovered in the cryptographic equipment responsible for securing cutting-edge weapon systems…
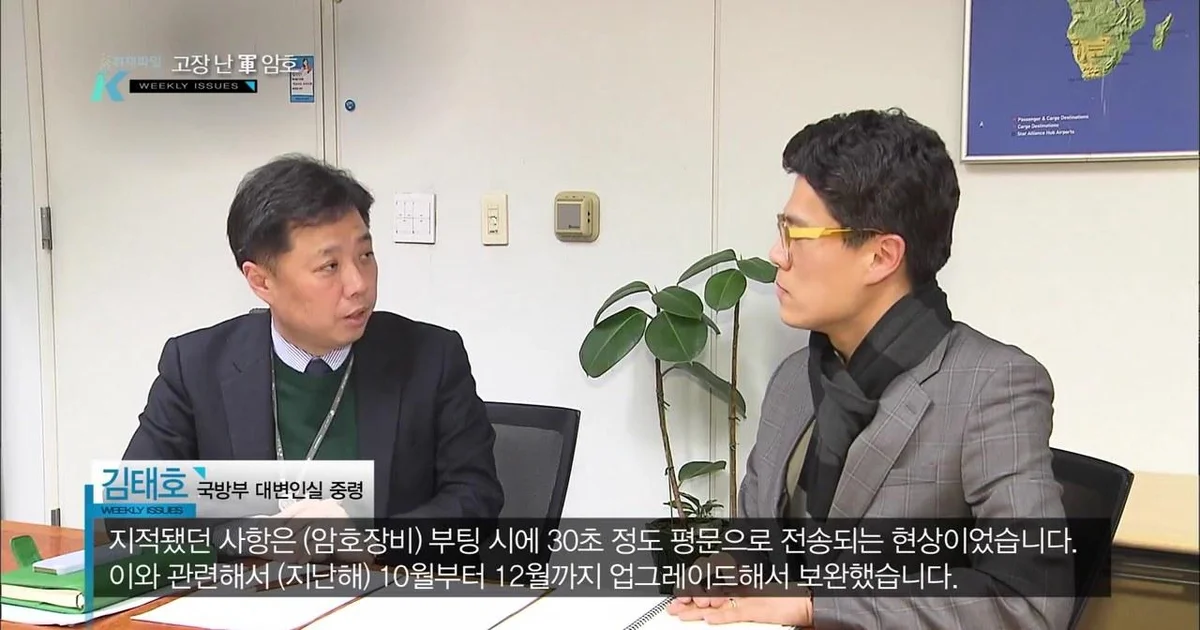
A fatal flaw has been revealed in the cryptographic equipment responsible for the security of cutting-edge weapon systems, such as the radars of Aegis ships and F-35 stealth fighters operated by our military. It was confirmed that the cryptographic equipment, essential for the communication networks of the Army, Navy, and Republic of Korea Air Force, failed to properly encrypt data, causing Level 2 military secrets to be exposed as original plaintext.
"The server is taken over the moment of login"... Security hole warned by experts
According to a KBS documentary video, the M-model cryptographic equipment installed in military security computers showed errors where the original text of classified documents was sometimes transmitted as is, despite the requirement to encrypt and transmit data. The place that first discovered this problem was the Republic of Korea Air Force. In 2013, the Republic of Korea Air Force conducted tests under the same conditions as the operational communication networks currently in use through internal testing. They connected the cryptographic equipment to both the server and the client to test whether classified documents were converted into code, but they produced a report after confirming that data sent as a combination of numbers appeared as the original text even after passing through the cryptographic equipment during the transmission process. The Republic of Korea Air Force reported that security is vulnerable because the original content of the files can be checked, and that the cryptographic equipment cannot guarantee secrecy.
The seriousness of the problem was further specified through the testimony of field experts. A security company expert, who presented analysis data at an informal meeting attended by high-ranking officials of the Defense Security Command and cryptographic officers at the time, pointed out, "The moment a server administrator logs in, the encryption is undone in the cryptographic communication equipment." He continued, "If that happens, the server is taken over by a hacker in an instant, and it is a very serious level of flaw that can buy an attacker a significant amount of time." The expert emphasized that the seriousness of the problem was shared during the meeting where even the cryptographic officers of the Defense Security Command were summoned.
Ministry of National Defense of South Korea's explanation of 'testing environment fault' and belated admission of the flaw
As the flaw was revealed, criticisms arose that the response from military authorities was inadequate. When this issue was raised during National Assembly audits, the Ministry of National Defense of South Korea initially attempted to downplay or conceal the problem, claiming that the phenomenon of plaintext exposure even after passing through the cryptographic equipment was "a problem caused by the testing environment being incorrectly set up." According to the response of the Director of Intelligence in the video, the Ministry of National Defense of South Korea explained the test results from April 2014 as a mistake in system installation, and subsequently concluded through working-level meetings that there was no abnormality in the equipment.
However, as continuous criticisms continued, the Ministry of National Defense of South Korea finally admitted to the flaw. The Ministry of National Defense of South Korea belatedly revealed that improvements were needed, such as the temporary failure of encryption during the early stages of the network cryptographic equipment's operation. An official in the video explained, "There was a phenomenon where it was transmitted as plaintext for about 30 seconds during booting," and explained that equipment upgrades were carried out from October to December to supplement the problem. After the security vulnerability was confirmed, the military instructed units and agencies operating cryptographic equipment to necessarily operate security equipment equipped with firewalls and intrusion prevention systems. Additionally, they took measures to supplement operational flaws, such as instructing each military branch to remove internal connections and complete initialization before reassembling when the cryptographic equipment must be rebooted.
Contracts worth tens of billions of won and suspicions of 'Ampia Connection'
Beyond the security flaw, issues regarding the transparency of the equipment supply process also surfaced. The company that manufactures and supplies the cryptographic equipment to the military and government departments was established in 1999 and has signed contracts worth tens of billions of won, supplying approximately 60,000 cryptographic security devices connected to various domestic computer servers. However, it became controversial that this process was conducted through private contracts rather than open bidding for security reasons.
In some parts of the defense industry, suspicions are being raised that some former military personnel or retirees from national research institutes exerted improper influence during this process. These suspicions were also dealt with during the National Assembly audit process, and one expert raised the question of whether the specificity of the military lowered the threshold for security verification, stating, "If this had been procured as a civilian product, it would be a product that would not have passed inspection." As the flaw in the cryptographic system, which determines the victory or defeat of information warfare, intertwines with the opacity of the supply process, awareness of structural loopholes in the national security system is being demanded. Experts mentioned the case during World War II where the Allies decided the victory or defeat by decoding the Enigma code, emphasizing that a cryptographic system can be an important means that can bring down a nation.
Comments 0